Pre-launchWaitlist open
The mobile pentest console
that runs on your machine.
Static analysis, live device control, Frida instrumentation, network capture and a 23-mode AI copilot — one local-first workbench for Android and iOS apps. The browser is only the control plane: ADB, Frida and the decompilers run on your machine.
- Frida scripts
- 30
- 7 built-in + 23 community
- Copilot modes
- 23
- explain · hunt · bypass
- AI providers
- 7
- Ollama local + 6 cloud
- Secret detectors
- 36
- code · resources · .so
- Chain patterns
- 28
- found with zero AI tokens
- Report formats
- 5
- MD · HTML · PDF · DOCX · XLSX
- Potentialstatic signal
- Confirmedindependent evidence
- Validatedproven at runtime
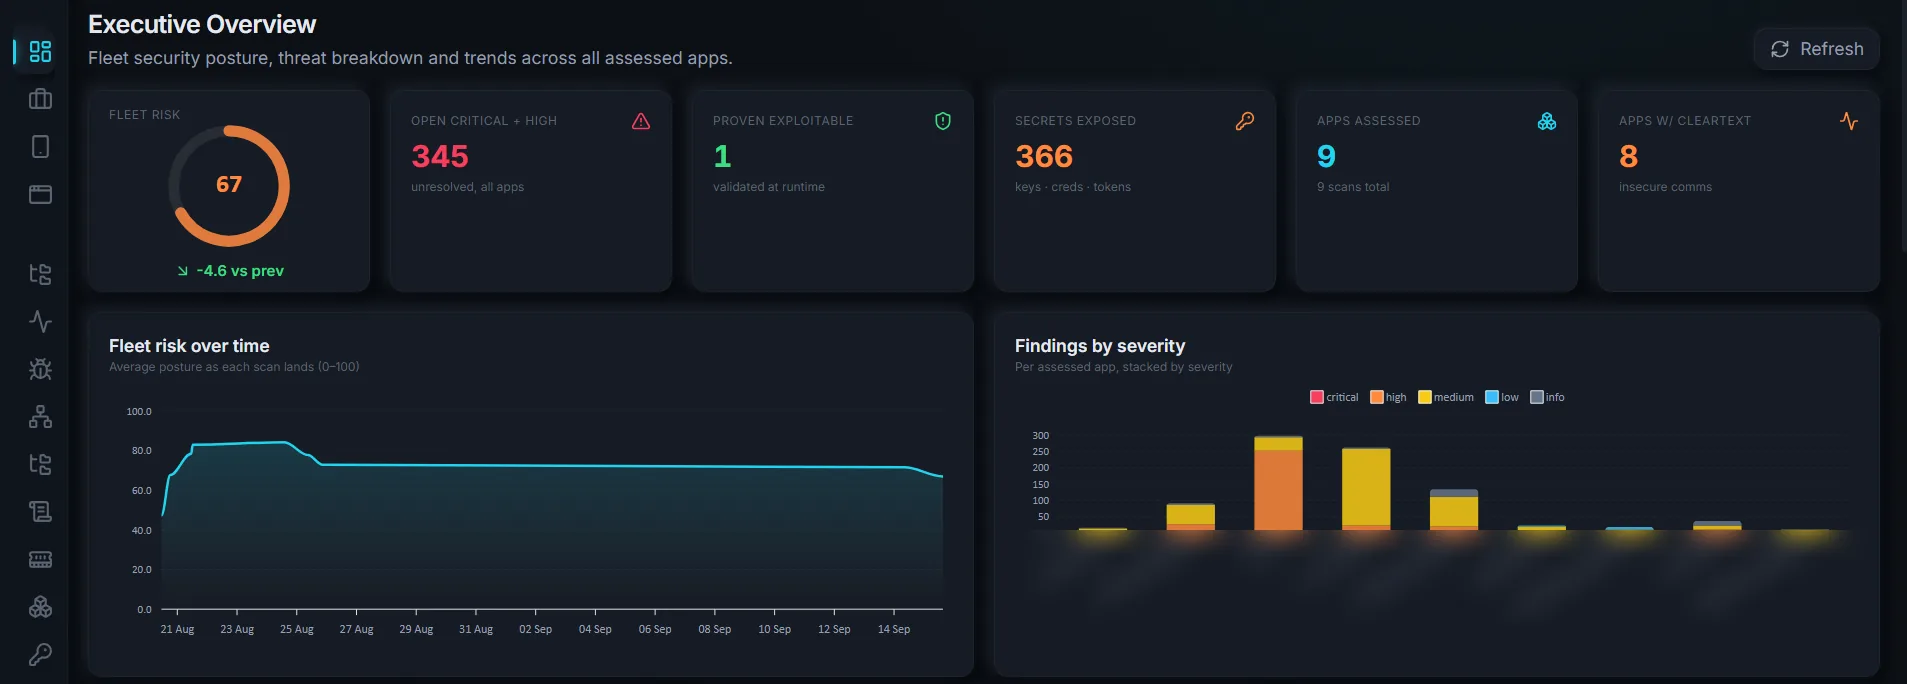
- Proven exploitable
- 1validated at runtime
- Secrets exposed
- 366keys · creds · tokens
- Apps assessed
- 9Android + iOS
01 / The fragmented stack
One assessment. Not eight terminals.
- adb
- jadx
- apktool
- frida
- mitmdump
One audited, allowlisted runner. Every tool call classified LOW / MEDIUM / HIGH, and never a raw shell.
02 / Local-first, by architecture
Nothing privileged leaves your machine.
127.0.0.1. Your device, ADB and Frida server stay on your desk and LAN. The only bytes that ever leave are opt-in calls you trigger.Settings · Privacy
Local-only mode
Flip it and MobLizer refuses cloud AI entirely. A persistent LOCAL / CLOUD indicator always shows the current mode.
Bring your own model — 7 providers
- Ollamalocal
- OpenAI
- Anthropic
- OpenRouter
- DeepSeek
- ScaleMax
- Kimi
Local-only mode refuses every cloud provider. Ollama runs entirely on your machine.
The runner allowlist — 9 programs, nothing else
- adbLOW
- fridaMEDIUM
- jadxLOW
- apktoolLOW
- apksignerLOW
- keytoolLOW
- javaLOW
- mitmdumpMEDIUM
- gitMEDIUM
Never a raw shell. Args are passed as a list, every call is timeout-bounded and audited, and HIGH-risk actions (like installing a system CA) need explicit acknowledgement.
03 / From APK to findings
One resilient static pipeline.
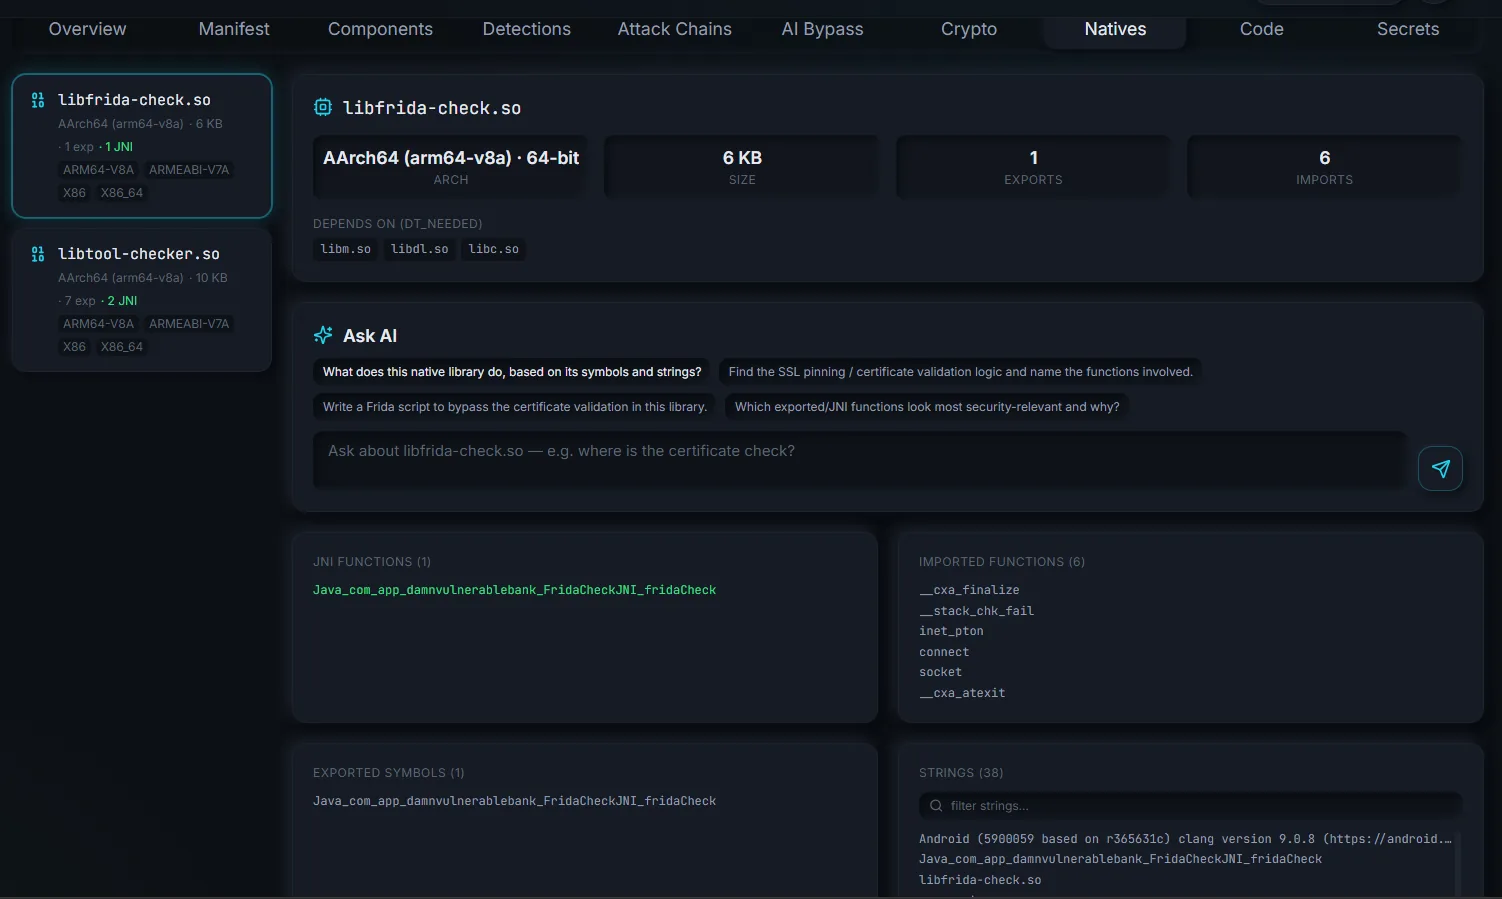
apktool → jadx → manifest → certs → natives → secrets, plus a source-to-sink taint engine. Each stage is isolated: if one fails, the rest keep going.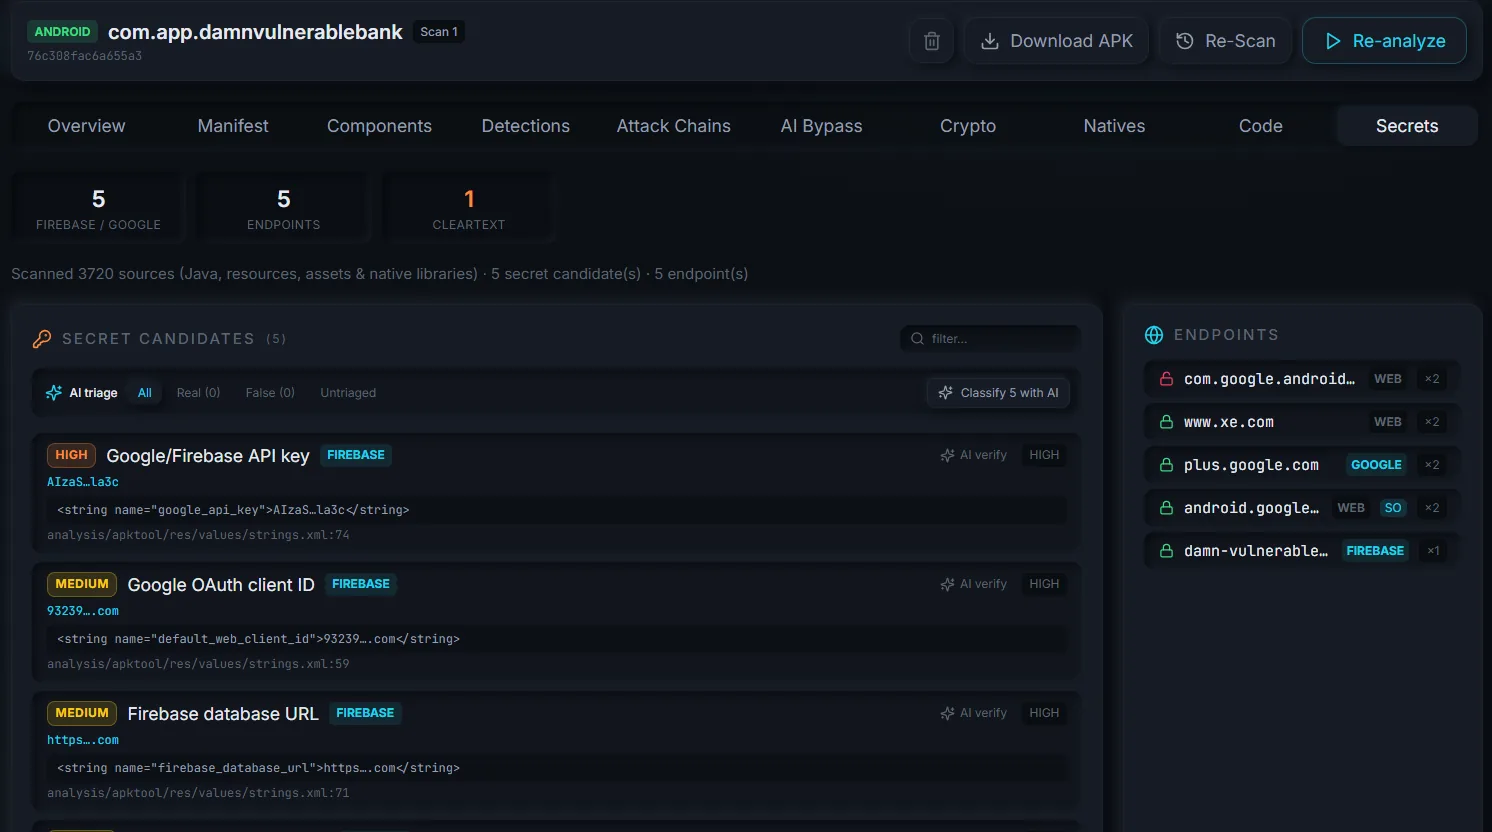
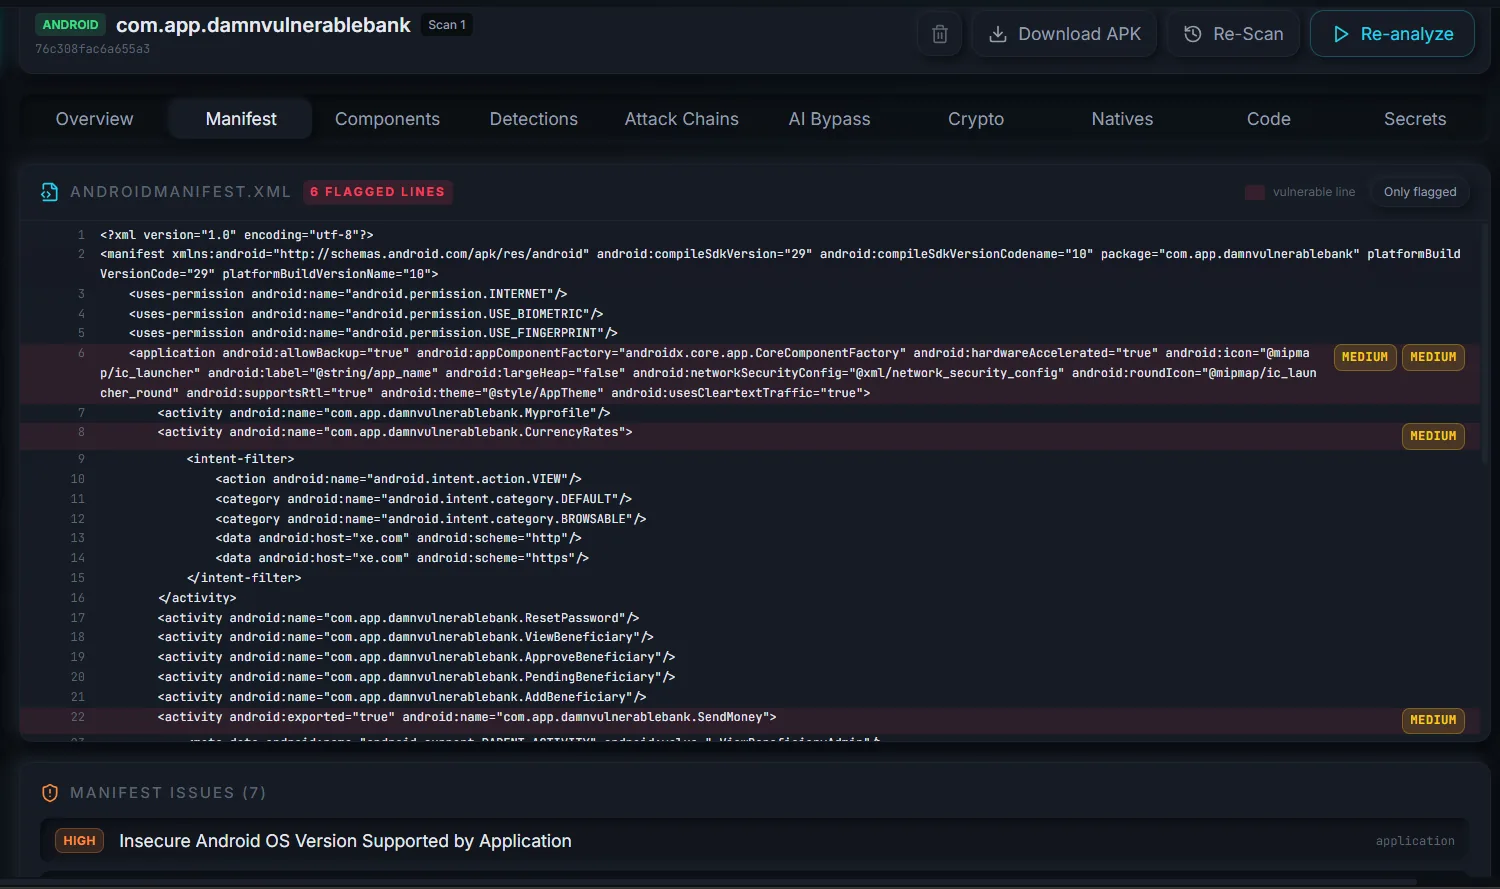 6 flagged lines
- 54 findings rules
- 82 behaviour rules
- 36 secret detectors
- 28 chain patterns
04 / Android, deeper than the APK
Go deeper than the manifest.
Component intent intelligence
For each exported component, MobLizer reads the extras and URI it consumes, then hands you a ready-to-run adb command — cited to its source line.
Dependency-free native analyser
A built-in ELF parser reports architecture, exported and imported symbols and strings — no radare2, nm or objdump. Works the same on Windows.
36 secret + endpoint detectors
Regex and entropy detectors sweep decompiled Java, resources, assets and native .so strings. JWTs are decoded to show their algorithm and claims.
Source-to-sink taint engine
A real dataflow engine seeded from exported components finds confused-deputy paths — intent redirection, provider SQLi, file theft (CWE-926 for improper exports).
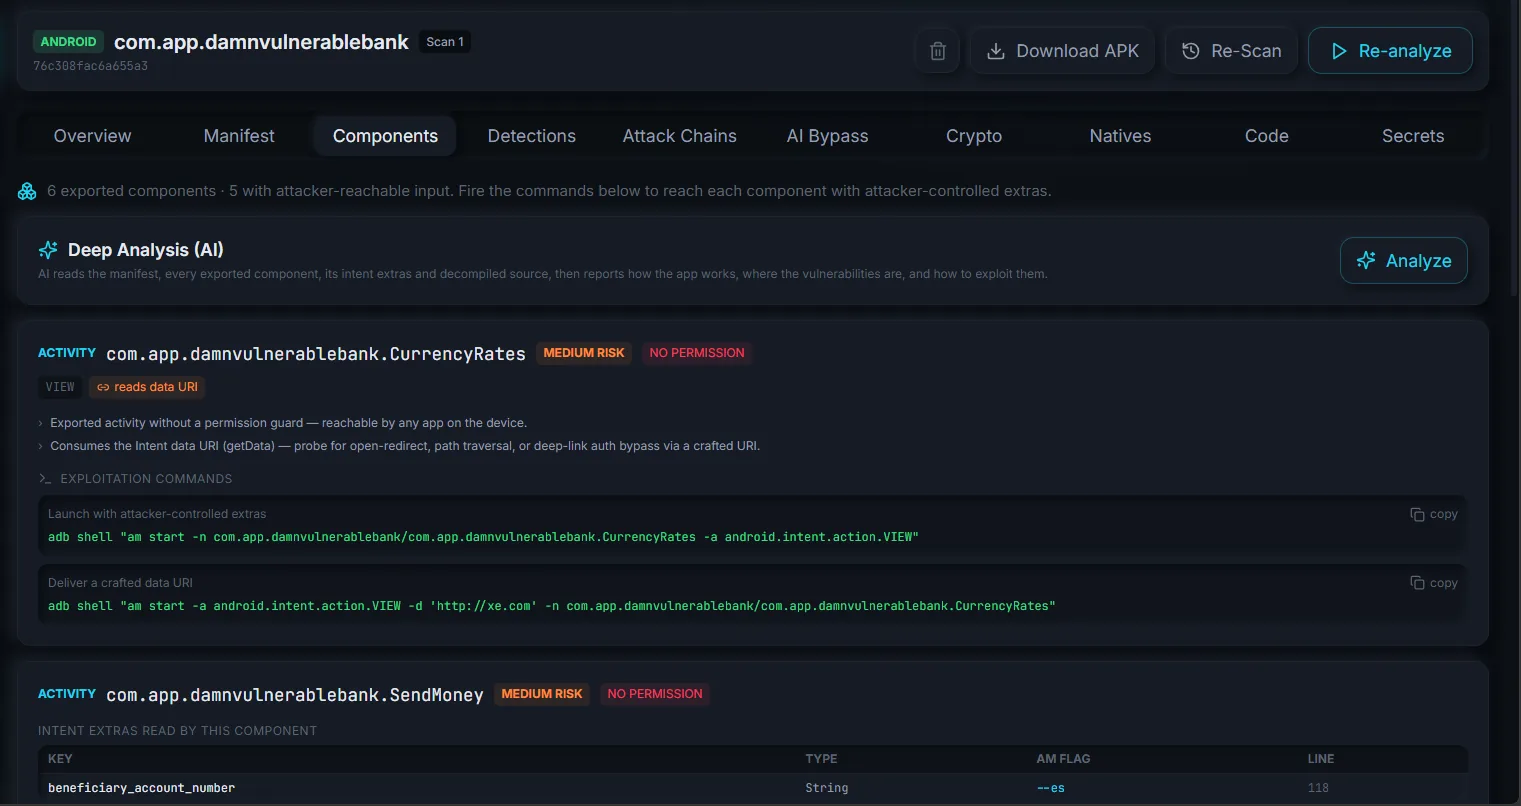
# Reach an exported activity with attacker-controlled extras
adb shell am start -n com.app.target/.CurrencyRates \
  -a android.intent.action.VIEW \
  -d 'https://xe.com' --es beneficiary_account_number 1337
Every extra is cited to the source line it was read from.
05 / Don't just collect evidence
AI that drafts runnable Frida — grounded in the app's real code.
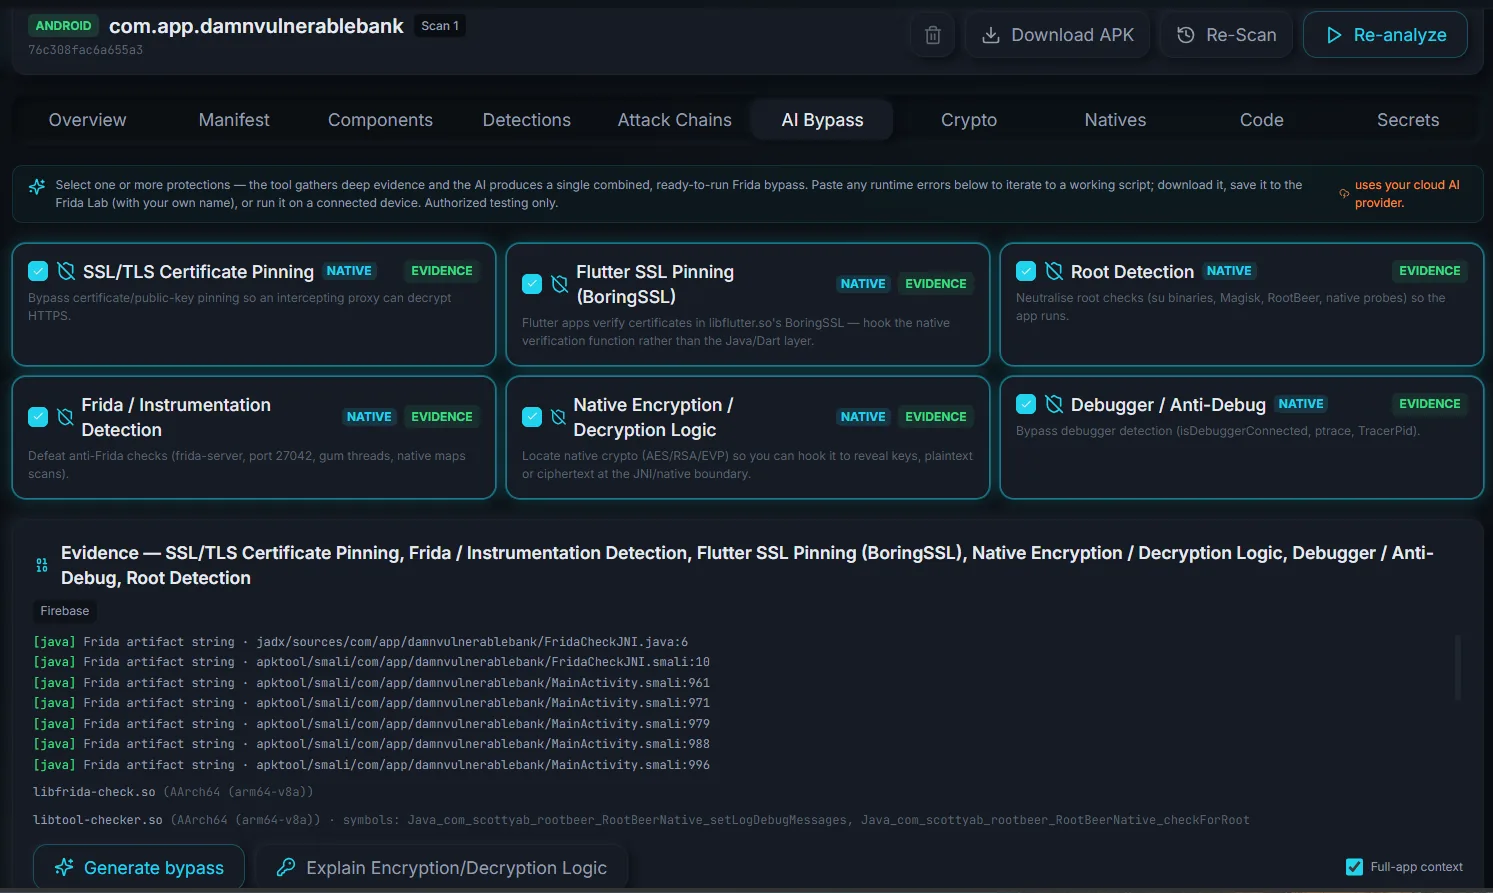
The orange note is deliberate: generating a bypass uses your chosen cloud AI provider — shown before it runs, and disabled entirely in local-only mode.
Java.perform(() => {
  const Intent = Java.use('android.content.Intent');
  Intent.getStringExtra.implementation = function (key) {
    const value = this.getStringExtra(key);
    console.log('[intent] ' + key + ' = ' + value);
    return value;
  };
});
Press Run to stream the instrumentation output.
Illustrative output — the scripts and commands are real and correct.
30 Frida scripts · 7 built-in + 23 curated community, attributed
06 / Connect findings into paths
From primitives to attack paths.
Attack chains · this scan
3 chains
from 9 extracted primitives
Discovery is deterministic and spends no tokens. AI is invoked only on the chain you choose to investigate, so cost tracks your attention.
- highAUTHunverified
Deep-link → WebView token/parameter injection
An exported deep-link entry feeds attacker-controlled data into a WebView, enabling parameter/token injection or loading attacker content into a trusted origin.
component.deeplink_entrywebview.js_enabledAnalyze with AI - highNETWORKunverified
Token capture via cleartext / broken TLS trust
The app permits cleartext traffic or trusts all certificates on at least one path, so an on-path attacker can read or modify traffic — capturing tokens in transit.
network.cleartext_allowedAnalyze with AI - mediumIPCunverified
Privilege/behaviour abuse via exported components
Exported components accept attacker-controlled intents/extras without a permission guard, letting another app drive protected behaviour or inject data.
component.exported_unguardedAnalyze with AI
07 / Your device, in the workspace
Your device becomes part of the workspace.
live mirroring · DVBA, a deliberately vulnerable test app
- Android
- 11 · API 30
- ABI
- arm64-v8a
- Security patch
- 2021-12-01
- RAM free
- 2.1 GB
- Mirror the screen and send input over ADB
- Stream structured logcat with severity filters
- Browse the filesystem, SQLite and SharedPreferences
- Every tool call policy-gated and audited
08 / See what the app sends
See what the app actually sends.
mitmdump over Wi-Fi, inspect every flow, and install the system CA on rooted devices — a HIGH-risk step, gated and acknowledged.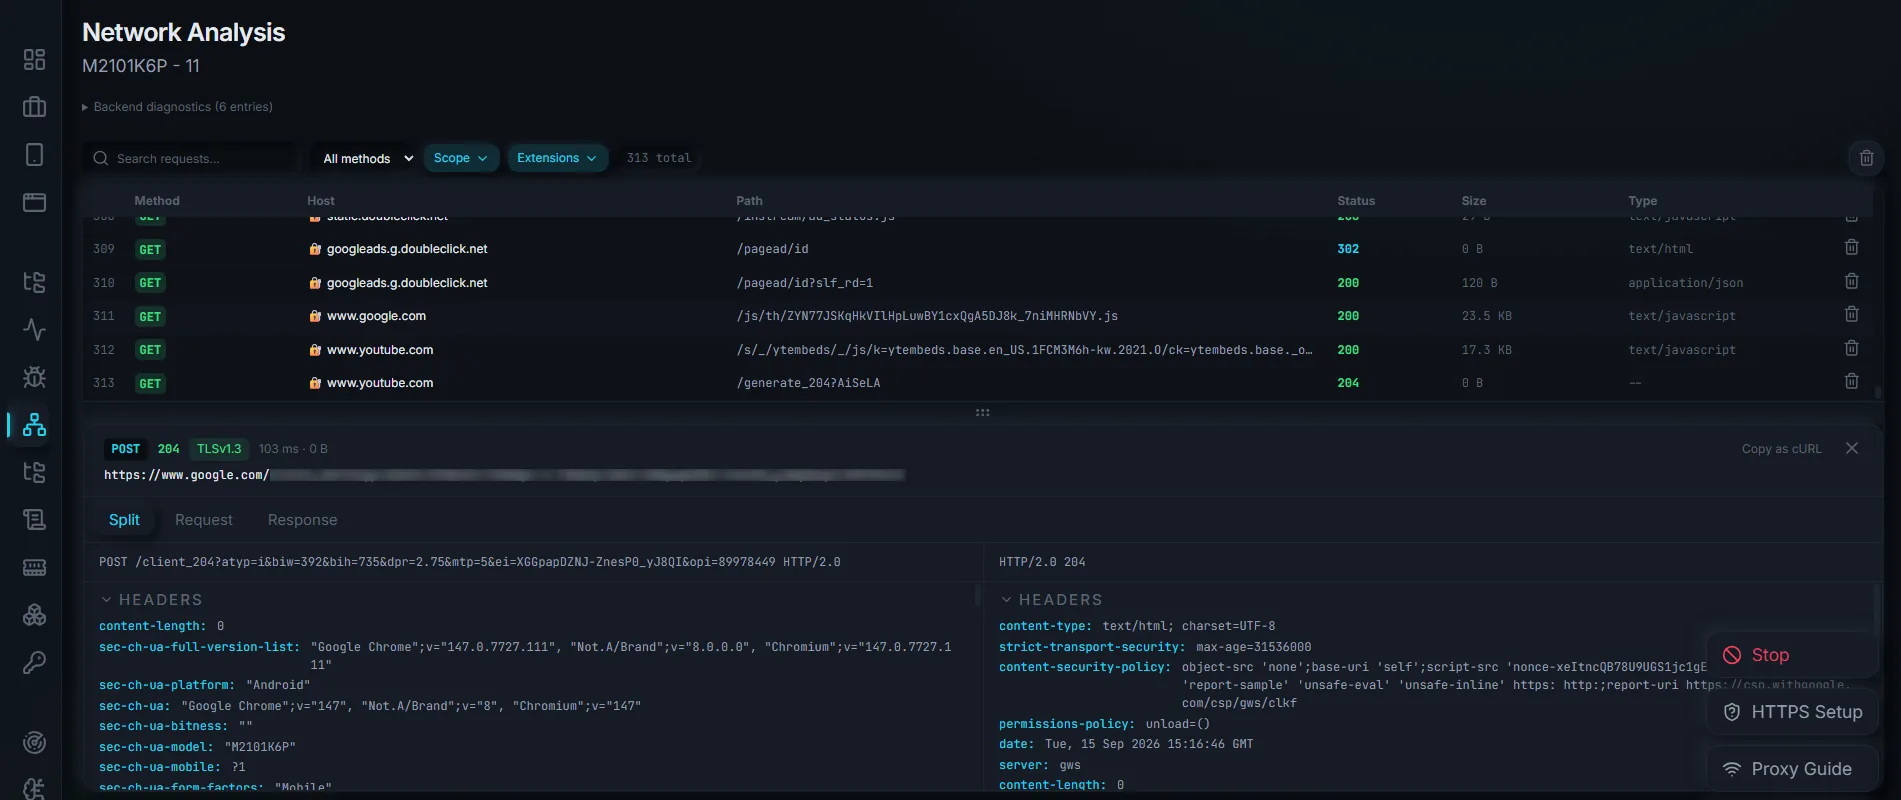
One-click HTTPS interception on rooted devices installs the mitmproxy CA via a Magisk module, a tmpfs overlay, or the user store — classified HIGH-risk and acknowledged before it runs.
09 / Client-ready, and iOS without a Mac
Client-ready reports. And iOS, without a Mac.
Business impact
Every finding leads with plain-language impact — what an attacker gains and why it matters to the business — so a report reads without a translator.
IPAs analyse statically on any OS: Mach-O protections, entitlements, ATS, URL schemes and built-in Objective-C class metadata — static analysis only, no runtime or keychain dumping. FairPlay-encrypted binaries are flagged; plist, entitlement and framework checks still run.
- 7
- URL schemes
- 70
- Frameworks
- 12
- Usage strings
- 2
- Secrets
- 12
- Endpoints
- 0
- Cleartext
No macOS required — works on any IPA.
The mobile attack surface
Android. Under. Scope.
MobLizer is pre-launch. Join the waitlist for early access — one launch email, no spam.
Local-first · CWE / OWASP Mobile Top 10 / MASVS · pre-launch